¶ The A.T.V. assessment: assets, threats and vulnerabilities
The A.T.V. assessment is the second step in Diri's risk assessment process, and a central part of risk identification as defined in ISO/IEC 27005. Within the scope set at registration, you identify and rank the assets, threats and vulnerabilities that apply. In step 3, the bowtie uses these rankings to suggest probability and impact, so your estimates can be traced back to an assessed level instead of being set by hand.

Risk arises when a threat exploits a vulnerability in an asset — anything of value to the organisation, physical or intangible, whether that value is financial, operational or reputational.
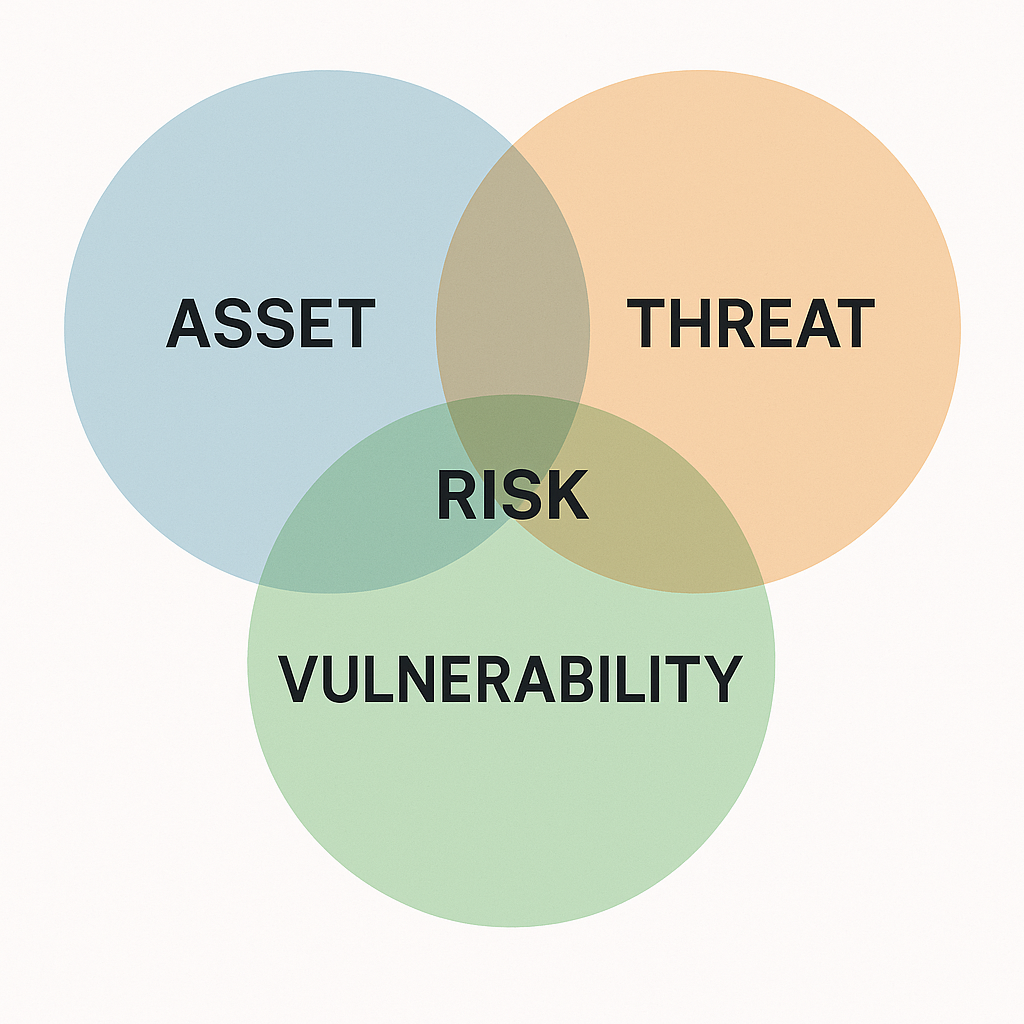
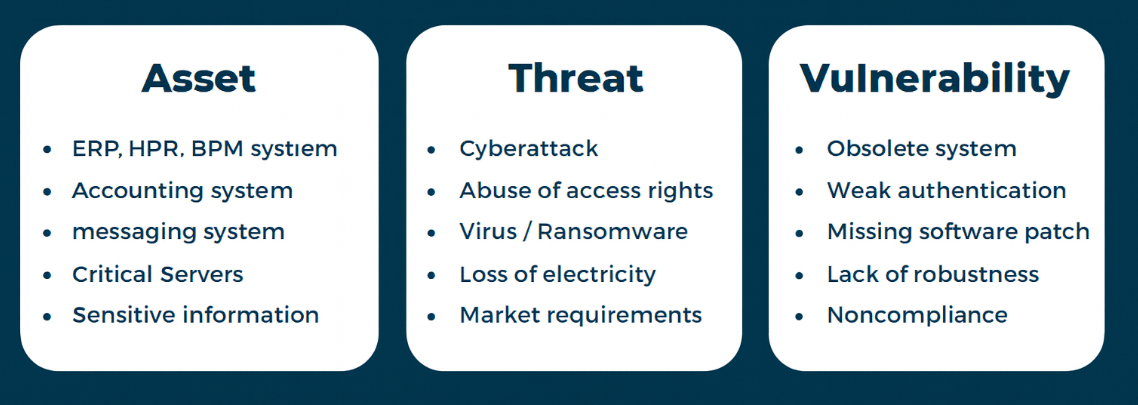
In Diri, the findings from the A.T.V. assessment are used in the bowtie risk assessment:
- A cause needs both a linked threat and a linked vulnerability to get a recommended probability.
- A consequence needs an affected asset to get a recommended impact.
The step has three tabs: Assets, Threats and Vulnerabilities. Each tab tells you what is still missing for the bowtie to make recommendations. Anything you add here is stored in your organisation's central registers and is available to every assessment in the organisation, not only this one. When you are done, click Finish asset evaluation.
Have many assets, threats or vulnerabilities in a spreadsheet already? They can be imported, see Bulk import.
¶ Asset evaluation
Asset evaluation determines which assets need protection. The main purpose is to identify and prioritise critical assets and assess their need for protection.
A proper asset evaluation helps you:
- Get a clear overview of where critical assets are in your organisation.
- Understand risk — what happens if an asset becomes known, altered or unavailable?
- Determine system criticality and define security or continuity requirements.
- Use assets as the basis for consequence evaluation in the bowtie (step 3).
To evaluate assets:
- Open step 2 on the risk assessment dashboard and select the Assets tab.
- Click Add asset to register a new asset, or Add existing asset to reuse one from the register.
- Fill out the form: Asset name, Asset type, Who owns the asset?, Asset description and the evaluation (see below).
- Use Why did you evaluate the asset this way? to document your reasoning. Justifications for high classifications are especially important for later revisions.

¶ Information assets (Cyber security module)
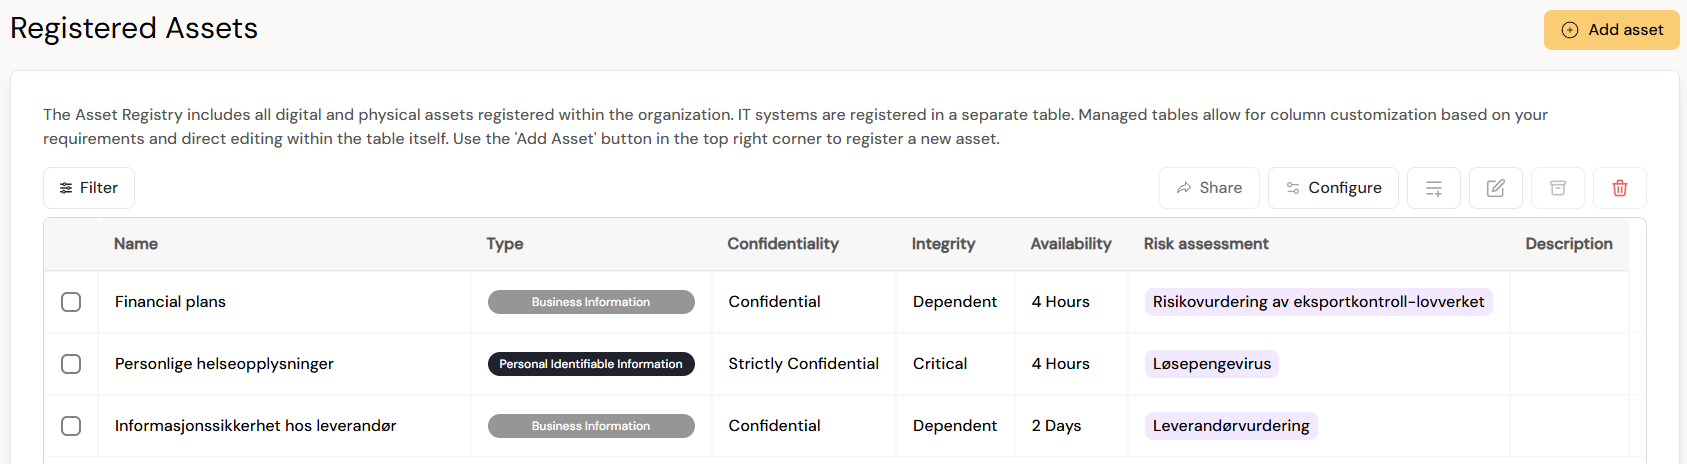
For information security risk, the focus is on information assets that are stored, processed or transmitted in the object being assessed — often an IT system. Diri uses an information classification approach that evaluates the need for:
- Confidentiality - How confidential is the asset according to your organisation's classification levels?
- Integrity - How crucial is it that the asset is accurate and complete?
- Availability - How long can the asset be unavailable before it causes further consequences?
Confidentiality, integrity and availability are abbreviated CIA. The classification describes the consequences if something happens to an information asset, and is therefore used as a measure of system criticality. The highest level among the assets sets the level for the system: if a system contains an asset classified at level 4, the system is also at level 4.

¶ Information classification levels
Before you start, make sure the classification levels and their descriptions are defined for your organisation. Diri suggests four levels with descriptions that you can use or change. While assessing, you can open the level descriptions directly from the form to see what each level means.
Administrators configure the levels in Settings → General → Asset classification. Choose between 3 and 6 levels and name them according to your existing policy. The scale applies to every module. See Settings.

¶ Business assets (Operational risk module)
For operational risk, the concern extends beyond information to business assets — the people, processes, services and physical or organisational components that keep the organisation running. The object being assessed is often a business process, a service or an organisational unit.
Business assets are evaluated by their importance: How important is the asset for the organisation?, from Not Important to Extremely. The result shows where treatments will have the greatest effect on continuity and resilience.
¶ Custom business asset types
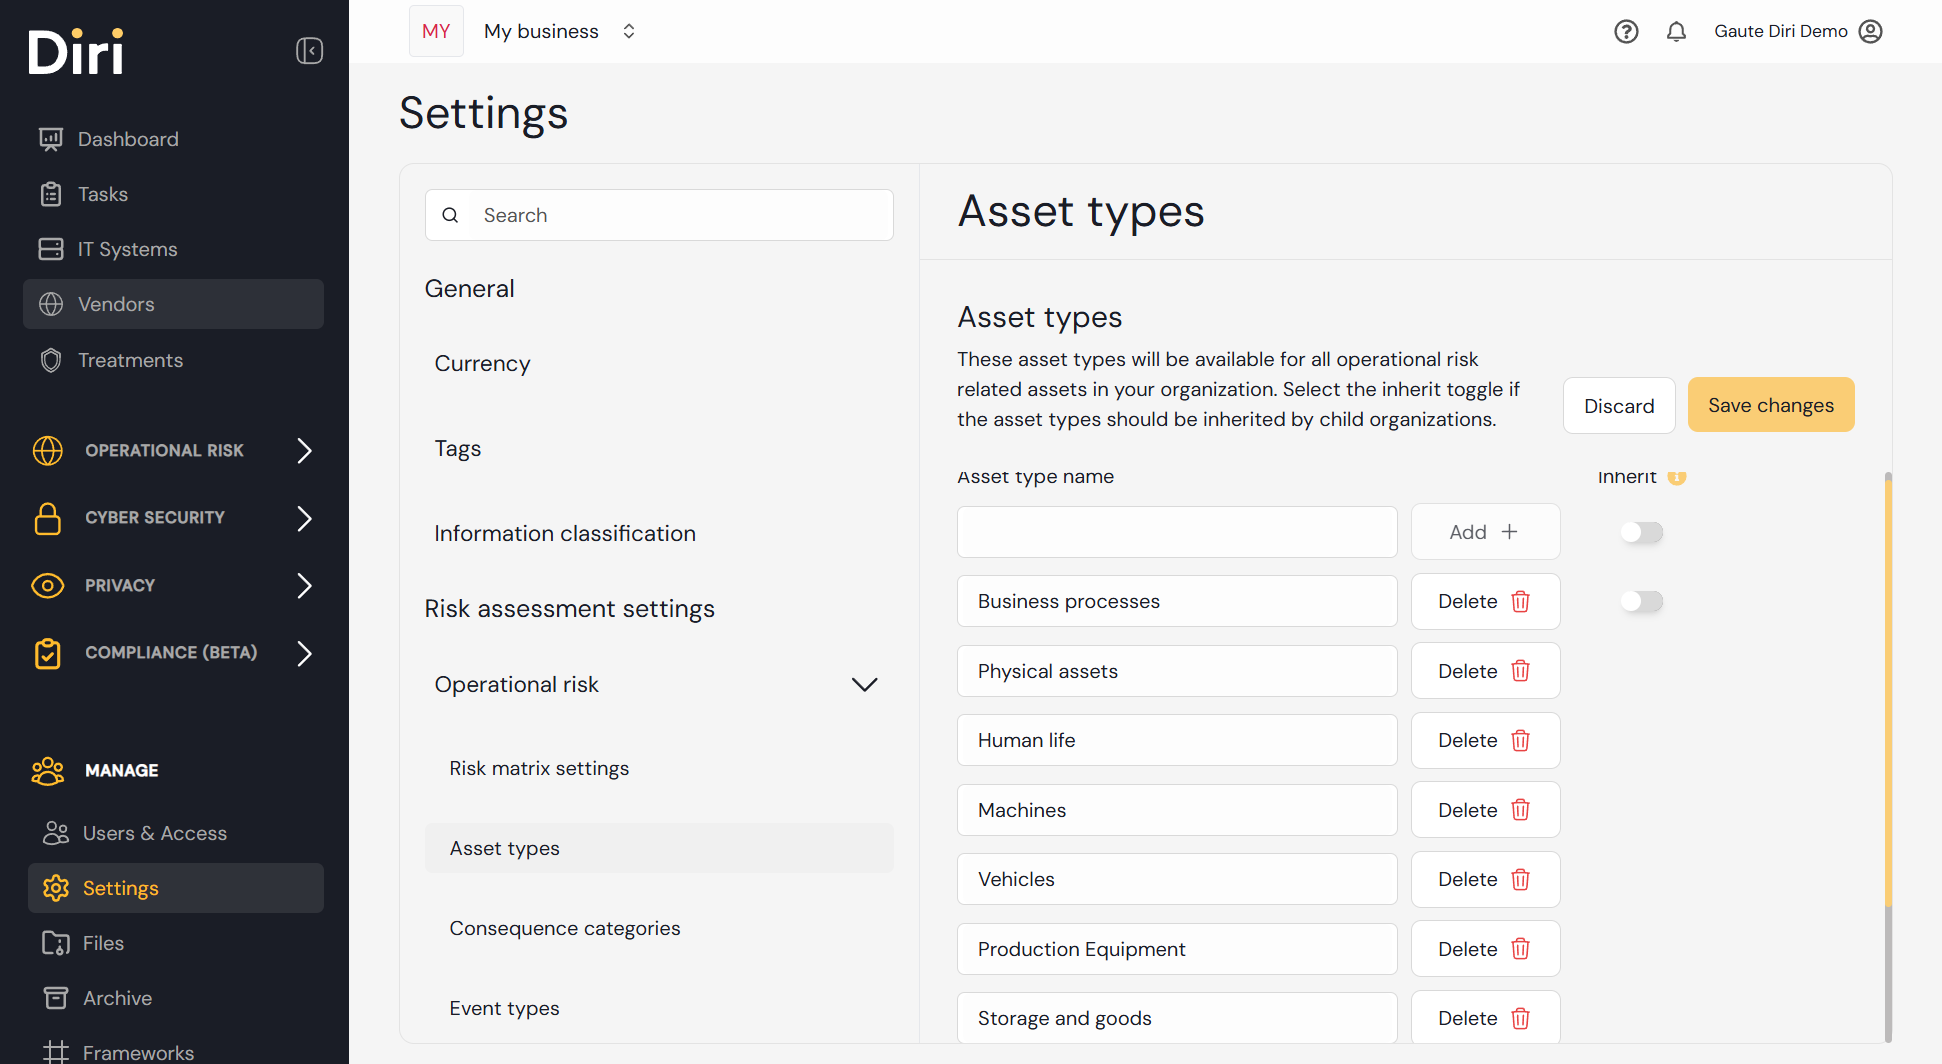
Business asset types are set in Settings → Operational risk → Asset types. Here you can add and customise asset types for your organisation. Turn on inheritance if sub-organisations should use the same asset types.
¶ Outcome of the asset evaluation
The asset evaluation gives you a clear overview of the critical assets and their classification. The assets are added to the asset registry of the module (Information assets under Cyber security, Business Assets under Operational risk) and are used when you evaluate consequences in the bowtie.
¶ Threat assessment
A threat is anything or anyone capable of causing harm to values, resources or objectives. Threats may be intentional or unintentional and originate from people, organisations, natural events or system failures.
On the Threats tab, click Add threat to register a new threat or Add existing threat to reuse one. Describe the threat, choose a Threat category and set the Threat level (0–100).

The threat level set on the threat itself is the shared recommendation used wherever the threat is applied. To use a different level in one assessment, set Threat level for this risk assessment instead. This changes the level for this assessment only, without changing the shared recommendation.

All threats are stored in the central threat register (Threats in the left menu) so they can be reused in other risk assessments.
¶ Vulnerability assessment
A vulnerability is a weakness or condition that makes your assets more susceptible to threats, such as technical flaws, missing controls, human factors or organisational gaps.
On the Vulnerabilities tab, add new or existing vulnerabilities and set the exposure level to indicate how easily the weakness could be exploited. As for threats, you can set Exposure level for this risk assessment to adjust the level for this assessment only.

Vulnerabilities are stored in the central vulnerability register (Vulnerabilities in the left menu) and can be reused in other assessments.
¶ Summary
In step 2, you identify the assets, threats and vulnerabilities — the core components of risk as defined in ISO/IEC 27005:
- Assets are classified by confidentiality, integrity and availability (information assets) or importance (business assets), and are the basis for the recommended impact of a consequence.
- Threats get a threat level and vulnerabilities an exposure level. Together they are the basis for the recommended probability of a cause.
- Everything is stored in central registers and can be reused across assessments.
Continue with Step 3 - Bowtie risk assessment.