¶ Why the five-step process
Diri is developed to help organisations perform structured and efficient risk assessments. It gives a clear overview of risks and risk-reducing measures, so that your organisation keeps an up-to-date risk picture.
Diri's processes and methods are built on recognised standards such as ISO/IEC 27005, refined to be practical and user-friendly.
When you open a risk assessment, its dashboard shows the Registration and assessment process with five steps. We recommend completing the steps in order. Each step is completed manually, for example with Finish asset evaluation, Finish risk assessment or Finish treatment plan. You can also choose Save and close and finish later.
¶ The five steps
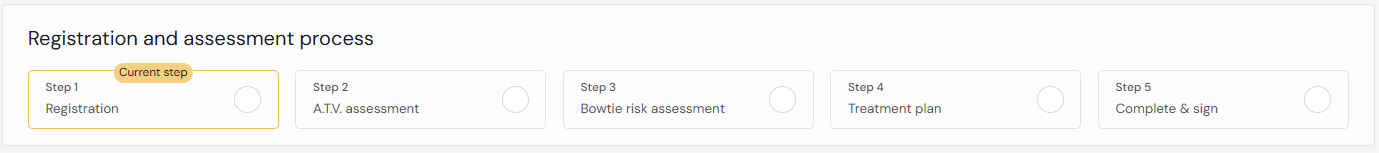
Step 1 – Registration
Define the object of the assessment — for example an IT system, a vendor, an asset or an operation — and describe its purpose, delimitations, participants and who is responsible. Read more.
Step 2 – A.T.V. assessment
Identify and rank the assets, threats and vulnerabilities within scope. They are stored in your organisation's central registers and are used in step 3 to suggest probability and impact. Read more.
Step 3 – Bowtie risk assessment
Build the bowtie: unwanted events, their causes and consequences, and the treatments that reduce probability or impact. Diri recommends probability and consequence levels from what you registered in step 2. The risks appear in the risk registry. Read more.
Step 4 – Treatments & cost-benefit
Choose which treatments to include in the plan. Diri ranks treatments by how much risk they remove and shows what the plan costs and how the risk picture moves. Read more.
Step 5 – Complete & sign
The decision-maker signs the treatment plan and accepts the residual risk. Signing records the risk owner and starts the review period. You can also send the assessment to someone else for signing. Read more.
By following these five steps, Diri helps your organisation move from risk identification to informed, documented decisions.
¶ Other ways to get started
- Start from a template to reuse a set of assets, events, causes, consequences and treatments.
- Import an existing risk assessment from Excel or CSV straight into the bowtie work surface, see Bulk import.
- Start from a dependency simulation: when you explore what happens if a system goes down or is compromised, you can record the result as a risk, see Dependencies.